Knowledge Hub

Knowledge Hub

Field notes, breakdowns and lessons on OSINT, KYC, due diligence and fraud risk - written by our analysts.

Due Diligence & Background Checks

The co-pilot of flight FZ1073: what a background check would have found on the day he was hired
Due Diligence & Background Checks

The co-pilot of flight FZ1073: what a background check would have found on the day he was hired

On 30 September 2026 the co-pilot of Flydubai flight FZ1073, from Dubai to Tel Aviv, attacked the captain in the cockpit and tried to take the controls. We asked one question: was there public information online, before he was hired, that a background check would have found, and did it carry warning signs?

Read full postShow less

We fixed the list of indicators before searching. We tested two dates: his hiring by Flydubai in February 2026, according to the Wall Street Journal, and the day of the attack. We ran 28 Google searches limited to pages dated before the hiring date, to see what a check run at the time would have returned. The search covered English and Arabic, including archives of deleted content.

What was online before he was hired

We found none of the pre-set indicators of violent radicalization. The violent material appeared about nine hours after the attack.

But the Internet Archive preserved about 3,000 tweets from a deleted X account of his, from 2021 and 2022. Under ProfCheck's method, they carry four negative behavioural indicators:

• Demeaning women.

• Hostility to foreigners.

• Imposing religious norms on others, with support for violent punishment.

• Deliberate deception with fake identities.

How a check gets there

Sixteen name searches, in English and in Arabic, surfaced none of his pages from before the hiring date. A search by his username surfaced his accounts in the first results.

The username appears on a mirror page that carries his name in Arabic, and on his LinkedIn page. An analyst who reads Arabic and checks every result gets there. An automated name screen does not.

Reading in the language matters in the other direction too. The word "حماس" appears in his tweets twice, and both times it means "enthusiasm". A keyword filter would flag it as a finding. A reader who sees the context would not.

Where the strongest warning signs were

According to what has been reported so far, the strongest warning signs were not online:

• According to the Wall Street Journal, ABC and CNN, Oman removed him from flight duties over extremist views or extremist material.

• Royal Air Maroc said he completed theoretical training as part of a pre-employment process, and his application was not selected. His LinkedIn profile presented it as about seven months of employment.

• According to a Gulf diplomat, the checks before he was hired focused on criminal convictions, not on signs of radicalization.

• According to the Wall Street Journal, no one asked Oman about him.

But in my view, this is the central lesson of the case: a criminal-record check is not a background check. A contradiction between a candidate's profile and a former employer's answer is a standard employment verification finding, and here it was within reach.

Our conclusion: under ProfCheck's method, the archived tweets alone carry four negative indicators. Together with the offline facts, a ProfCheck report on the hiring date would have given the employer clear grounds not to hire him as a pilot. The report does not recommend or disqualify; the decision stays with the employer.

What this means for employers

In practice, this means, among other things:

• Search in the candidate's language and by username, not only by the name in English.

• Include archives in the check. Deleted content is not necessarily gone.

• Have every result read in context by someone who reads the language.

• Verify employment with former employers, including changes of role and the reason for leaving, and compare the answers with the CV and the profile.

• Treat conduct as a finding, and keep association out. Family, nationality, religious practice and political opinion are not indicators.

• Check again after hiring, in roles with access to aircraft, sites or systems.

It is important to note: the person this case discusses is a suspect. As of 4 October 2026 he had not been charged in court or convicted, and no authority had officially confirmed his identity. The review used public sources only.

Another case study using the same method, on the recording device in OpenAI's executive boardroom: https://profcheck.co/knowledge/case-study-openai-recording-device/

The full report, with a link to the source of every finding, is available for download.Download the report

Article page
Can criminal record information found online be used in a background check?
Due Diligence & Background Checks

Can criminal record information found online be used in a background check?

One of the most complex questions in background checks is not how to find information.

Read full postShow less

It is what you are allowed to do with it after you have found it.

The difficulty stands out especially when, during a background check based on open sources, information surfaces that relates to a criminal offense, an investigation, a legal proceeding or conduct of a criminal nature.

It can be a court ruling published in a legal database.

An old article on a news site.

An announcement by a public authority.

A report about an indictment.

A publication about a conviction.

Or even a public document that describes a factual event without using the words "criminal record" at all.

In such a situation a natural question arises:

If the information did not come from the police and was not pulled from the criminal register, but was found in an ordinary internet search, is it permitted to pass it on to the employer and take it into account in a hiring decision?

The answer is not a simple yes or no.

And the reason is that you have to separate three different questions:

1. Is it permitted to collect the information?

2. Is it permitted to pass it on to the party making the decision?

3. Is that party permitted to use it in an employment decision?

These are three entirely different stages.

First of all: what is "criminal information" under the law in the first place?

Israel's Criminal Information and Rehabilitation of Offenders Law, 2019, defines "criminal information" as information from the criminal register and from the police register.

The criminal register includes, among other things, details of convictions and certain decisions listed in the law.

The police register includes other types of information, such as pending cases and additional police information in accordance with the provisions of the law.

The initial implication matters:

Not every piece of information describing criminal conduct is necessarily "criminal information" in the technical sense of the law.

A newspaper article is not the criminal register.

A court ruling published to the public is not the police database.

An announcement by a public authority does not become a police register just because it describes an offense.

But this is exactly where the complexity begins.

The source of the information is not the end of the discussion

It is very easy to reach the following conclusion:

"If I found it on Google, I am allowed to use it."

That is a dangerous conclusion.

The Criminal Information Law does not deal only with how a person obtains information.

Section 38 provides that whoever is not entitled to receive certain criminal information, or criminal information at all, shall not take it into account in making a decision.

The section goes on to provide that "additional information relating to the said criminal information" shall not be taken into account either.

In other words, the fact that information came from an open source does not necessarily detach it from the restrictions that apply to the use of criminal information.

The test is not only:

"Where did the information come from?"

You also have to ask:

"What did we actually learn from it?"

And:

"What do we intend to do with this information?"

This is a critical distinction.

OSINT cannot become a bypass route for obtaining information whose use the law was designed to restrict.

In other words:

If an employer is not entitled to receive certain information from the criminal register, it is wrong to assume that it can simply reconstruct that same information through a search of open sources and then use it as if the restriction did not exist.

But the opposite direction is not correct either

Here it is important to avoid the opposite mistake.

The fact that a public source describes criminal conduct does not automatically turn every detail in it into information that must not be collected, reported or considered.

A background check may uncover factual information with clear significance for risk assessment.

Sometimes that information is also connected to a criminal proceeding.

The question is not only which legal label can be attached to it.

You have to understand the context.

Is it a conviction?

An investigation?

An indictment?

A closed case?

An acquittal?

A claim made by a party in a civil proceeding?

A factual finding by a court?

A press report whose outcome is unclear?

Or documented conduct relevant to the role, even if the legal proceeding itself is not the focus of the check?

Each of these cases is different.

An example: a candidate who is supposed to manage money

Suppose a person is a candidate for the role of CFO.

The role includes signing off on payments, access to bank accounts, permissions in financial systems and responsibility for significant sums of money.

During a background check, a public and reliable court ruling is found describing that person's past involvement in an act of financial fraud.

Here, two extreme reactions would be problematic.

The first reaction:

"It is a public court ruling, so we are automatically allowed to pass it on and recommend against hiring."

That conclusion is too broad.

The second reaction:

"There is a connection to a criminal offense here, so we are not allowed to relate to the information at all."

That conclusion is also too broad.

A professional background check needs to break the finding down.

What exactly did the ruling determine?

Is it a conviction or only a description of a claim?

When did the event take place?

What was the person's part in it?

Did the proceeding end in a way that changes the meaning of the finding?

Are there additional sources that corroborate it?

And the central question from a risk management perspective:

What is the connection between the finding and the role being assessed?

When a person is about to receive control over money, a reliable finding concerning fraudulent financial conduct may carry far clearer significance than in a role with no access to funds, assets or financial permissions.

But here too, relevance to the role is not a "get out of the law" card.

It is part of the check, not a substitute for the legal analysis.

Relevance is a central condition, but not the only condition

This is perhaps the most important distinction.

In the background check world we are used to thinking in terms of relevance.

Rightly so.

The purpose of a background check is not to collect every detail that can be found about a person.

The purpose is to identify information with a real connection to the risk arising from the role.

For example:

A history of financial fraud may be highly relevant to a role that includes access to funds.

An incident of information misuse may be relevant to a role with permissions to sensitive databases.

Violent behavior may take on special significance in a role that includes responsibility for the safety of others.

A material breach of trust can be relevant to a role in which the employee will receive broad independence and access to sensitive assets.

But relevance alone is not enough.

Even highly relevant information can be information whose use the law restricts.

So the correct order is:

Legality first.

Relevance after.

And not the other way around.

Not every press mention equals a "criminal record"

There is another professional problem as well.

The internet almost never provides a complete legal picture.

You can find an article from 2018 saying a person was arrested.

But what happened afterwards?

Was an indictment filed?

Was the case closed?

Was the person acquitted?

Is it even the right person?

Was a correction to the article published?

Did a higher court overturn the ruling?

A background check that collects the first mention and stops there can be worse than not conducting a check at all.

Especially when the information has the potential to harm a person.

That is why such a finding requires verification, context and updating.

The acquittal is a good example of the trap

Suppose a search of a candidate's name brings up dozens of articles about a high profile criminal trial.

At first glance the impression is severe.

But after reading the ruling it turns out the person was acquitted.

If the analyst settles for the old headlines, they are effectively creating a picture that is the opposite of the legal reality.

This is one of the reasons a background check cannot amount to a keyword search.

You have to understand the sequence of events and the outcome.

The age of the information matters too

A finding that is one year old is not necessarily the same as a finding that is twenty years old.

The Criminal Information Law itself is built, among other things, on a concept of limitation periods, expungement and rehabilitation.

The purpose is not only to protect information.

It is also to allow a person not to carry forever the full weight of an event from their past.

So when old information appears online, the fact that the internet "remembers" it does not mean an employer must necessarily remember it the same way.

This is especially true for information whose influence the law itself sought to reduce over time.

And what about information that is not a conviction?

Here even greater caution is required.

An arrest is not a conviction.

An investigation is not a conviction.

An indictment is not a conviction.

A closed case is certainly not a conviction.

An article about a suspicion is not proof that the suspicion was correct.

And yet, an OSINT search can bring up all of these.

That is why a professional background check cannot settle for the words:

"We found a negative publication."

You have to say exactly what was found.

Who published it.

When.

What its legal status is.

And what happened afterwards.

The difference between:

"The candidate was convicted of fraud"

And:

"In 2019 it was reported that the candidate was questioned on suspicion of fraud"

Is enormous.

Three questions to ask before such a finding goes into a report

When information connected to a criminal proceeding surfaces during a background check, it is right to separate three layers.

1. Is it permitted to collect it?

Is it information from a legitimate public source?

Was the way the information was obtained lawful?

Is there no attempt here to bypass a legal restriction through a third party?

2. Is it right and permitted to report it?

Even information found lawfully does not have to enter the report automatically.

Its reliability, currency, severity and relevance have to be examined.

You also have to consider whether passing it on could put the decision maker in a position of being exposed to information the law does not allow them to take into account.

3. Is the employer permitted to use it in the decision?

That is a separate question.

An employer may be authorized to receive one type of information and not another.

Certain roles are subject to special arrangements.

Certain bodies hold powers that an ordinary private employer does not have.

And sometimes the law allows information to be taken into account only under certain conditions.

So there is no single answer that fits every organization and every role.

Amendment 10 to the law demonstrates exactly this principle

In 2026 a new and narrowly focused arrangement concerning certain terrorism offenses was added to the law.

Under the conditions set, the law allows an employer to ask the police for a notice stating whether or not an adult candidate has a criminal record entry relating to a serious terrorism offense or to certain offenses under the Counter-Terrorism Law.

The request is conditional on the candidate's written consent, and the notice does not provide the employer with the full details of the register.

The amendment came into force on August 24, 2026.

The very fact that the legislator needed to create such a specific route illustrates an important point:

Access to criminal information for employment purposes is not a matter of "there is consent" or "I found the information".

It is a matter of authority, conditions and purpose.

So what is the role of an OSINT-based background check?

A background check is not a substitute for the criminal register.

And it is not supposed to be a way to reconstruct it.

Its role is far broader and different.

OSINT can uncover information about:

Conflicts of interest.

Companies and business connections.

False claims in a resume.

Professional history.

Sanctions.

Connections to high risk parties.

Civil proceedings.

Media reports.

Public statements.

Unusual business activity.

Behavioral patterns.

Information related to trustworthiness, when it is relevant to the role and collected and analyzed lawfully.

And sometimes, within that space, information with a connection to the criminal world will surface as well.

At that point the professional responsibility is not to make it disappear automatically, and not to rush to pass it on either.

The responsibility is to understand exactly what was found.

The question is not only "what did we find?"

It is:

What is the source of the information?

What is its level of reliability?

What is its legal status?

Is there a later development?

How old is the finding?

Is it the right person?

Is it permitted to pass it on?

Is the employer permitted to use it?

And what is its real connection to the risk arising from the role?

Only after all of these questions are answered can you decide whether the finding should be included in the background check, and in what form.

The bottom line

"Public information" and "information that may be used in a hiring decision" are not synonyms.

But "information relating to criminal conduct" and "information that must never be reported" are not synonyms either.

Reality is more complex.

OSINT is not a way to bypass the Criminal Information Law.

But a background check should not ignore public, reliable and relevant information just because it relates to conduct that may be criminal.

The professional test lies in the combination of four things:

The legal framework.

The source and quality of the information.

The relevance to the role.

And the way the information will be used in making the decision.

Finding information online is the easy part.

Professionalism begins with the question of what is permitted, right and fair to do with it after we have found it.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page
Amendment No. 10 to the Criminal Information and Rehabilitation of Offenders Law: what changed, and what it really means for employers and background checks
Due Diligence & Background Checks

Amendment No. 10 to the Criminal Information and Rehabilitation of Offenders Law: what changed, and what it really means for employers and background checks

In February 2026, Amendment No. 10 to the Criminal Information and Rehabilitation of Offenders Law, 5779-2019, was approved. At first glance it looks like a relatively technical amendment, but in practice it has significant implications for the bodies entitled to receive criminal information, for job candidates, and for the way organizations manage recruitment risks.

Read full postShow less

At the same time, the amendment sharpens an important distinction that many people are unaware of: there is a separation between criminal information held in the criminal register and protected by law, and factual, public information found in open sources (OSINT), which is not part of the criminal register at all. It is precisely this distinction that makes OSINT-based background checks a more important tool today than ever before.

What did Amendment No. 10 change? The amendment adds a new mechanism of a “notice regarding the existence of a criminal record entry,” through the new Section 16A of the law. In certain cases, instead of disclosing the full content of the criminal record, the authorized body will receive a notice stating that a criminal record entry exists, in accordance with the arrangements set out in the law. In addition, this notice was defined as part of the term “criminal information.” The purpose of the amendment is to continue strengthening the principle of rehabilitation of offenders, while balancing the public interest against a person's right to rehabilitate.

What does it mean for employers? For most employers, the basic legal situation has not changed. Even today: an ordinary employer may not require a candidate to present a criminal record; it is prohibited to require a candidate to obtain information from the police on the employer's behalf; and only bodies expressly authorized by law may receive information from the criminal register, and only to the extent set by law. In other words, even after the amendment, most employers cannot base their decision-making process on the criminal register.

But this is where the common mistake begins. Quite a few people believe that if you cannot obtain a criminal record, you are not allowed to know anything about a candidate's past. This is not the correct interpretation. The law regulates access to the criminal register and to criminal information managed by the state. It does not prohibit locating factual information that has already been lawfully published in open sources. This is a very important legal distinction.

What is the difference between a criminal record and open information? A criminal record is information managed in the criminal register of the Israel Police, and access to it is regulated by law. By contrast, information such as judgments published in legal databases, official court publications, Israel Police spokesperson announcements, State Attorney's Office announcements, publications by regulatory authorities, credible news articles, tender and disqualification notices, liquidation, receivership or legal-proceedings documents, public business information, and publications of sanctions or international blacklists does not constitute “criminal information” as defined by law merely because it describes a criminal event or a conviction. This is public information that was lawfully published, and therefore it is not part of the criminal register itself. Of course, the use of such information must also be carried out in accordance with privacy protection laws, the prohibition of defamation, and the principles of relevance, proportionality and good faith.

This is where OSINT-based background checks come into the picture. A quality background check does not try to circumvent the law and does not try to obtain confidential information. On the contrary. It operates solely through public and lawful information sources. When professional OSINT is performed, it is sometimes possible to locate substantive information that is not accessible through the criminal register, for example: convictions published in judgments, involvement in fraud affairs that received publicity, indictments published lawfully, insolvency proceedings, significant civil proceedings, problematic business relationships, conflicts of interest, ties to high-risk companies or parties, indications of fraud or impersonation, and public behavioral patterns with occupational significance. Sometimes it is precisely this kind of information that gives the employer a broader picture than the mere existence of a criminal record.

Does this replace a criminal record? No. These are two entirely different tools. The criminal record is official state information. OSINT is not a criminal register and does not claim to be one. Its purpose is to identify indications of risk from public information that can be verified, cross-referenced and professionally assessed. Therefore, in many organizations, especially in sensitive positions, OSINT checks do not replace the checks prescribed by law, but rather complement them.

The practical meaning for employers: Amendment No. 10 continues the legislator's trend of strengthening the protection of people's privacy and the principle of rehabilitation. However, it does not eliminate employers' duty of care toward their employees, their customers and the organization. Therefore, the more restricted access to official criminal information becomes, the greater the importance of conducting quality background checks based on open, lawful, relevant and verified information.

The challenge for the employer today is not to obtain more information. The challenge is to know how to distinguish between information that may not be received and public information that is permitted, and even worth considering, as part of an informed decision-making process. It is also important to remember that any use of information originating in OSINT must be carried out in accordance with all relevant legislation, including the Privacy Protection Law, the prohibition of defamation, labor laws, and the principles of equality and proportionality. The mere fact that information has been published publicly does not automatically make it relevant or legitimate for every recruitment decision.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page Read the article
He had already been convicted before. That didn't stop people from handing him millions of shekels again
Due Diligence & Background Checks

He had already been convicted before. That didn't stop people from handing him millions of shekels again

This morning I read the article about Ido Samuel, who was previously convicted of fraud offenses, served a prison sentence, and after his release went back to managing money for private clients. Some of them lost significant sums.

Read full postShow less

This story is not just a story about investments, crypto or the capital market.

It is a story about a failure of due diligence.

Many people think a background check is only meant for hiring employees. In practice, it is no less important when choosing a business partner, an investment manager, a supplier, an advisor, or anyone who is supposed to be given access to money, information or assets.

In this case, some of the information was completely available in open sources: a criminal conviction for fraud offenses; a lengthy prison term; historical media coverage; legal proceedings and rulings; and business and public information that can be located through professional searching.

The problem is that finding the information is not enough. You have to know how to connect the dots.

An OSINT-based background check is not just about collecting data. The real value lies in the analysis and in understanding what the information means for the purpose of making a decision.

When you assess a person who is meant to manage your money or make financial decisions, the question is not only "Did he have a prior conviction?", but rather: Did he disclose it fully? Are there additional warning signs? Are there gaps between the public image and reality? And are there patterns that recur over the years?

Ultimately, most major frauds don't begin with technological sophistication. They begin with trust.

And before extending trust, it is worth conducting a professional background check based on open information sources, in order to make an informed decision grounded in facts rather than in personal impression or charisma.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page Read the article
The biggest mistake in background checks? Attributing information to the wrong person.
Due Diligence & Background Checks

The biggest mistake in background checks? Attributing information to the wrong person.

Many people think the main challenge in background checks is finding information.

Read full postShow less

In my view, that's actually the easy part.

The real challenge begins the moment after we've found the information: are we certain it belongs to the person we're actually checking?

In a world where millions of people share similar names, use nicknames, maintain multiple digital profiles and sometimes leave only partial traces, it's very easy to fall into the trap of a "quick identification."

I often come across cases where investigators, recruiters or managers see a problematic profile online, an old article or a negative mention, and rush to draw conclusions.

But a professional background check is not an exercise in gathering information. It's an exercise in verifying identities.

Before drawing conclusions, you have to verify: is it the same person? Does the geographic location match? Does the timeline line up? Are there additional identifiers that connect the data points? And are there independent sources that confirm the link?

The greatest danger isn't missing negative information. The greatest danger is attributing negative information to the wrong person.

A mistake like that can lead to flawed hiring decisions, damage to the reputation of an innocent person, and even legal exposure.

That's why one of the most important principles in open-source intelligence (OSINT) work is: first you verify. Only then do you conclude.

That's the difference between gathering information and pursuing the truth.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page
Doubt Is Your Lifeline
Due Diligence & Background Checks

Doubt Is Your Lifeline

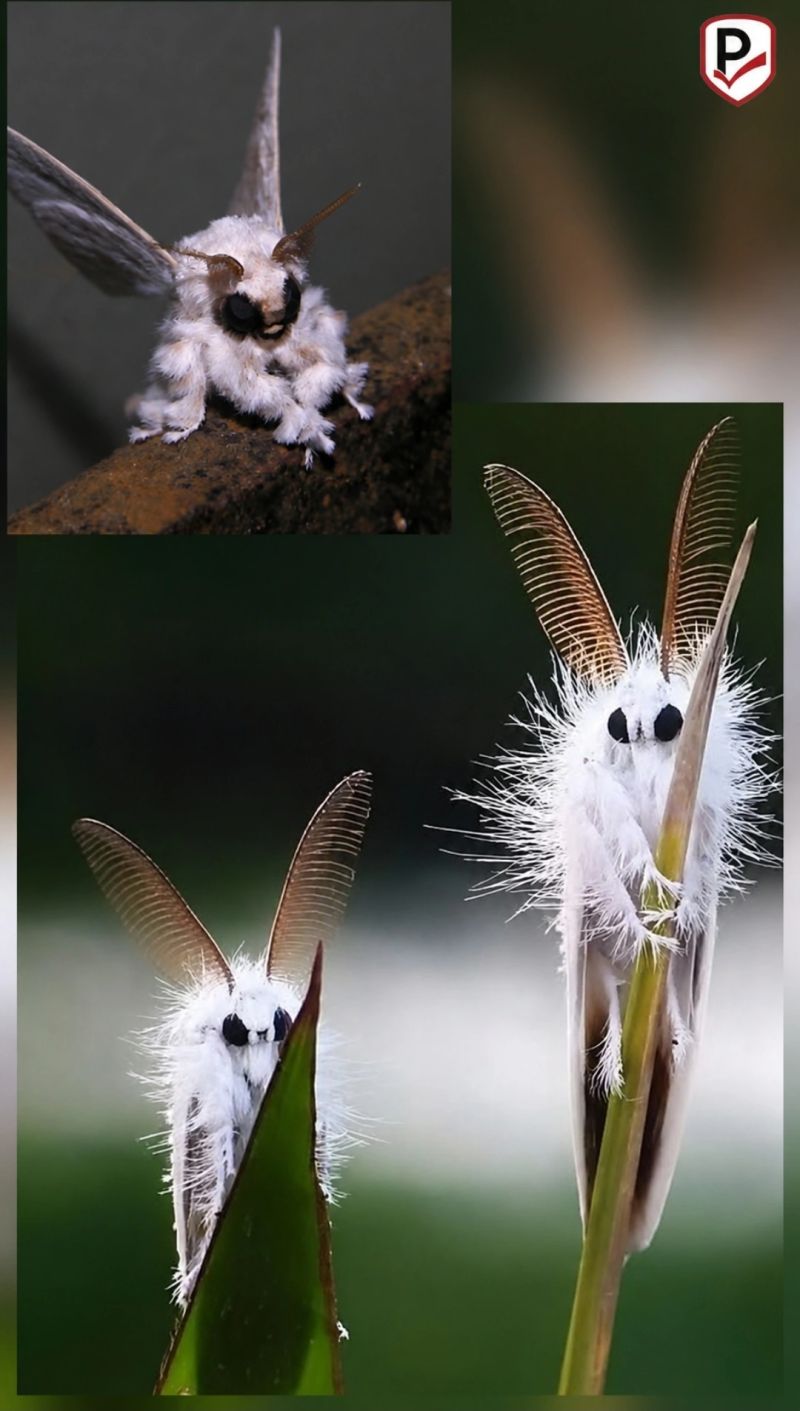
Today I came across a post about the "Venezuelan Poodle Moth" — a "poodle moth" that looks like a furry, cute creature out of an animated film.

Read full postShow less

At first it seemed completely credible. Photos, explanations, Google results, mentions on various sites including Wikipedia.

But the deeper I dug, the more I discovered that most of the story isn't grounded in anything at all. Some of the photos were wool sculptures by a Japanese artist. Others were images of entirely different species. And in practice, the only thing that truly exists is a single photograph of an unidentified moth taken in Venezuela (the image at the top left). There isn't even an official scientific recognition of such a species.

What's interesting here isn't the moth. It's the way information turns into "truth."

Today, search engines no longer rely solely on original sources. They are also fed by content created by AI, by automated summaries, by copying between sites, and by information that recycles itself again and again.

And what this means is that even if you try to do a "reverse trace" and check what the real source is, it becomes very difficult. Because at a certain point, the original source disappears, the information is copied hundreds of times, AI systems summarize erroneous information, and unverified content starts to look more credible than reality itself.

And this is precisely one of the great challenges in the world of background checks.

It isn't enough to know how to search for information. You need to know how to doubt information.

You need to understand: Who is the source? Is there any verification? Is this primary information or a copy? Is there a vested interest? And is everyone simply quoting one another?

In an era where AI can generate enormous quantities of convincing content, the ability to think critically becomes a critical professional asset.

This is exactly why professional background checks cannot rely solely on a quick Google search or on AI tools.

In the end, you still need people who know how to connect contexts, identify manipulation, understand what's missing from the picture — and above all, know when not to believe immediately something that looks credible.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page
When you're asked to "find the culprit" - but your capability isn't built for it
Due Diligence & Background Checks

When you're asked to "find the culprit" - but your capability isn't built for it

Recently I was approached with a very sensitive case involving the spread of fake content online.

Read full postShow less

The request was clear: locate the source of distribution, stop it quickly, and remove the content.

On the surface, this sounds like a classic open-source intelligence task. But that's exactly where the problem begins.

I want to share with you, with professional honesty, where OSINT is strong and where it simply isn't enough.

Where OSINT delivers real value: you can map how content spreads, identify groups, channels and distribution hubs, track recurring users across different platforms, and understand who is "pushing" the story forward. This provides a very important intelligence picture.

But here comes the critical limitation: you cannot identify with certainty who the person behind the account is, prove who created the content, access closed information (IP, devices, logs), or guarantee complete removal from the internet.

And when it comes to sensitive incidents, especially involving minors or privacy violations, the smallest mistake in identification can turn into a serious legal problem.

The real risk: the problem is not only technological - it is managerial. When you make promises like "we'll find who did it" and "we'll take everything off the web" without understanding the limits, that's a recipe for disappointment at best, and for damage at worst.

So what is the right thing to do in such cases? The right approach is always multidisciplinary: OSINT for mapping and understanding, DFIR for collecting evidence from devices and systems, legal support for approaching the platforms, damage control and prevention of repeated distribution, and continuous monitoring. Anyone who handles this alone, from a single angle, misses the picture.

The bottom line: open-source intelligence is a very powerful tool - but it is not magic.

Knowing what can be done is important. But knowing what cannot be done - that is what separates professional work from risk.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page
The problem is not a lack of information. The problem is noise
Due Diligence & Background Checks

The problem is not a lack of information. The problem is noise

Google's new capability to analyze information from the dark web using AI, and what struck me most is not the technology itself but the approach: no longer "more information", but smart filtering that understands context.

Read full postShow less

And this is exactly where many organizations fall short.

We live in an era of endless open information: forums, groups, leaks, small hints. But without real business context, without an understanding of what is relevant to a specific organization, it all turns into noise.

And this is not only in the cyber world.

It is exactly the same principle in the world of open-source intelligence.

I see it all the time: organizations think they need "more checks", "more sources", "more data". But the truth is the opposite. The real value comes from the ability to connect the dots.

For example: someone posts on a dark forum offering access to a system. They do not mention a company name. There are no clear keywords. Classic systems will not detect it. But if you understand the context, the type of system, the size of the company, the geographic location, the type of activity, suddenly it is no longer "general information". It is a very specific threat.

And now think about this in the context of insider threats.

Many times the threat does not start from within the organization. It starts outside, on the dark web, in forums, in groups. But it connects to people on the inside: an employee with access, a vendor with permissions, a candidate trying to get in.

Without a connection between external intelligence and an internal understanding of the organization, you miss the story.

And this is the truly important point: AI alone does not solve the problem. Relying on OSINT alone does not solve the problem.

Only a combination of real business context, human analysis that understands behavior, and technology that can operate at scale creates a real advantage.

Whoever keeps collecting information without understanding what is relevant to them will drown in the noise. Whoever knows how to connect the dots in time will identify the threat before it becomes an incident.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page
Amendment 13 to the Privacy Protection Law and international privacy regulations: Do they jeopardize the future of OSINT-based background checks?
Due Diligence & Background Checks

Amendment 13 to the Privacy Protection Law and international privacy regulations: Do they jeopardize the future of OSINT-based background checks?

In recent years, we have witnessed a significant tightening of privacy protection requirements around the world. Regulations such as GDPR in Europe, CCPA in California, PIPEDA in Canada, and additional legislation in many countries have created a new standard for managing personal information. In Israel, Amendment 13 to the Privacy Protection Law represents another significant step in this direction.

Read full postShow less

For organizations that conduct background checks based on open-source intelligence (OSINT), the question sometimes arises as to whether these regulations will make such checks impossible or undermine their effectiveness.

The professional answer is no.

Regulation changes the way in which the check is performed, but it does not eliminate the need for it, and it does not prevent the conduct of high-quality checks when they are carried out in a professional, lawful, and proportionate manner.

What is Amendment 13 to the Privacy Protection Law? Amendment 13 is intended to strengthen the enforcement capabilities of the Privacy Protection Authority and to align Israeli law with modern international standards. Among other things, the amendment grants the Privacy Protection Authority broader enforcement powers, significantly increases the level of financial sanctions, requires organizations to manage personal information more responsibly, increases the accountability of database owners and data processors, and strengthens the rights of data subjects. In practice, the implication for organizations is that violating privacy provisions may become a significant business, legal, and reputational risk.

How do privacy regulations affect background checks? The most common mistake is to think that privacy legislation prohibits the collection of information. In fact, most regulations around the world do not impose a blanket prohibition on collecting personal information. They require that collection be carried out on the basis of clear principles: a legitimate purpose, proportionality, transparency, data minimization, data security, and limited retention over time. In other words, the question is not "is it permitted to collect information?" but rather "what information is collected, why is it collected, and how is it used?".

The use of OSINT is not exempt from privacy laws. There is another mistaken perception according to which information published online is "free to use". The fact that information is found online does not negate the fact that it is personal information. For example: a LinkedIn profile, social media posts, news articles, business records, and forum content. All of these may be considered personal information and subject to privacy laws. Therefore, an organization conducting background checks cannot rely on the claim that the information was merely "public".

How can high-quality background checks be conducted in compliance with regulation?

Defining a clear purpose: A background check should be directly related to the risk that the organization seeks to mitigate. For example: detecting conflicts of interest, identifying past fraud, detecting behaviors that may harm the organization, examining reputational risks, and identifying problematic business relationships. Collecting information unrelated to this purpose may be considered a deviation from the principle of proportionality.

Collecting only relevant information: A professional check is not measured by the quantity of information collected but by the quality of the information. In many cases, an excess of information actually makes decision-making more difficult. The correct approach is to focus on information of genuine business value and to link it to the required risk assessment.

Using human analysts: One of the central problems in automated checks is the massive collection of information without context. A professional analyst knows how to distinguish between fact and opinion, cross-reference sources, identify errors in identification, understand cultural and linguistic contexts, and exercise judgment. Precisely in a world of stringent regulation, the value of the human element grows.

Transparency and consent when required: In recruitment processes or certain engagements, it is recommended to obtain explicit consent to conduct a background check. Even when the law does not fully require this, clear consent strengthens the legitimacy of the process and reduces legal risks.

Deletion of information and limited retention: One of the fundamental principles in most privacy regulations is limiting the duration of retention. After completing the check and making the business decision, one should examine whether there is justification for continuing to retain the information, whether the reports can be deleted, and whether only partial retention of the data is necessary. This approach reduces data security risks and lowers regulatory exposure.

The advantage of OSINT precisely in the age of privacy: Paradoxically, privacy regulations actually strengthen the standing of high-quality OSINT checks. In the past, many organizations relied on collecting information from numerous databases, some of which were legally problematic. Today, the emphasis is shifting to information gathered from open, lawful, documented, and verifiable sources. When the check is conducted professionally, it is possible to reach significant insights even without access to private or confidential information. In many cases, it is precisely the open information that provides the most important indications regarding behavior, business relationships, reputational risks, or conflicts of interest.

The key is Governance, not prohibition: The central message of Amendment 13 and of privacy regulations around the world is not "do not conduct background checks". The message is: conduct them responsibly. Organizations that build orderly work processes, adhere to proportionality, operate control mechanisms, and use professional analysts will be able to continue conducting highly effective background checks even under stringent regulation.

In fact, in a world where insider threats, fraud, AI-based impersonation, and conflicts of interest are becoming more complex, the need for professional background checks is only growing.

The new challenge is not to find information. The challenge is to know how to collect the right information, use it lawfully, and derive from it insights of genuine value for decision-making.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page

Insider Threats & Organizational Risk

The United Airlines pilot barred from entering Israel: what a background check would have found before hiring and during employment
Insider Threats & Organizational Risk

The United Airlines pilot barred from entering Israel: what a background check would have found before hiring and during employment

A background check on the day of hiring cannot detect a post that will be published two and a half years later.

Read full postShow less

The case of the United Airlines pilot who, according to an N12 report of 21 October, was barred from Israeli airspace, shows why an organisation's responsibility continues after hiring.

The attached report examines two questions: what could be found in open sources before he started work in November 2022, and what was published later in his employment.

In the sources checked, no negative content from before hiring was found.

Content supporting the Iranian regime and its missile programme was found in posts from June 2025, about two and a half years later.

The report also analyses a capture of a story from October 2025 in which the song Boom, Boom, Tel Aviv can be heard. The song praises the missile attack on the city.

The story was deleted after the exposure, and its attribution to the account was checked using a capture kept by a third party and a cross-check with content that remained on the profile.

The screen showed only Boom boom :). The meaningful message was in the soundtrack. A check limited to the text would have missed it.

Finding the account also took more than a name search: the full name did not appear on the profile, and the attribution was based on cross-checking professional details against other sources.

But not every published claim was substantiated. The check found no evidence of support for Hezbollah or for the 7 October attack. Nor did it find indications of intent, planning or a threat to commit violence. Origin, religion and language were not defined as "red flags".

In my view, this is part of the professional responsibility in a background check: to be precise both about what we found and about what we have no basis to determine.

A relevant finding justifies clarification and a risk assessment, and it needs to be examined in the context of the role and of all the information.

These are three things I recommend that security and HR managers take from the case:

• Define which roles require a periodic check of public information, and how often, according to the sensitivity of the role and the scope of the employee's access and authority.

• Make sure the check also covers stories saved to highlights, reposts and videos, with an understanding of the language and the context. A name search and reading captions may leave significant information out.

• Decide in advance who verifies a finding, who assesses what it means for the role, and how to conduct a fair clarification with the employee.

Collecting information is useful only when there is a clear process for handling it.

I am attaching the full report, with the sources, the cross-checks and the limits of the review.

The question I suggest every organisation ask: if relevant information about an employee in a sensitive role appears tomorrow, who is supposed to identify it, and who is responsible for handling it?

The full report, with a link to the source of every finding, is available for download.Download the report

Article page
The recording device in OpenAI's executive boardroom: what a background check would have found before hiring
Insider Threats & Organizational Risk

The recording device in OpenAI's executive boardroom: what a background check would have found before hiring

On 13 October 2026 the US Department of Justice announced the arrest of an OpenAI engineer. According to the criminal complaint, he planted a covert audio recording device in the company's executive conference room in San Francisco. We checked what a background check from public sources would have found, before he was hired and while he worked there.

Read full postShow less

According to the complaint, company staff found the device at the end of September 2026, plugged in behind a television in the room and wrapped in toilet paper. He had worked at the company as an engineer since about July 2025, and had no authority to enter the room. The Department of Justice does not allege that a foreign government was involved. OpenAI said it has seen no sign that model weights, source code or customer data were taken, and that he was fired.

As in our earlier case study on flight FZ1073, we fixed the method before searching. We checked two dates: the day before he was hired, and the day before the device was installed. We read the findings through two separate lenses: the US government's conduct-based insider-risk indicators, and ProfCheck's method. We also ran 23 Google searches limited to pages dated before the hiring. The search covered English and Arabic.

What we did not find

No criminal record, no sanctions, no hostility to an employer and no support for violence. We read 262 of the 284 posts on his X account, and none of them fits the negative behavioural indicators in our method.

Two red flags, public before he was hired

The first: employment dates contradicted by a record. On his LinkedIn profile, his work at Meta ends in 2022. But in January 2025 an internal Meta code change was published in Meta's open-source repositories, from a Meta email address, under his username. The record was public about five months before he joined OpenAI. Google does not surface it. It is found only by searching his code history on GitHub.

The second: an outside role alongside the job. In February 2025 he joined a Riyadh venture capital fund as a venture partner, and the role continued while he worked at OpenAI. The role was announced publicly, so it was not hidden from the public. Whether he disclosed it to his employer is not known.

Under our method, a contradiction in employment dates and the non-disclosure of a conflict of interest, if that occurred, are indicators of unreliability. They do not prove wrongdoing. They are red flags that call for a clarification with the candidate before a decision: an explanation of the dates, a written list of outside roles, and verification with the former employers. Whether that clarification would have changed the decision cannot be known.

Where the warning signs about the act itself were

According to the complaint, every warning sign about the act was inside the building:

• Cameras recorded him near the room on ten different dates in September.

• He searched the company's own systems for where and when the leadership meets.

• An account linked to him asked a chatbot how to build a covert, encrypted recorder.

And in my view this part matters even more. A background check from public sources helps decide whom to hire. It cannot see what an employee does once inside. That is what an internal insider-risk program sees: access control, cameras and the logs of internal tools.

What this means for employers

In practice, this means, among other things:

• Verify employment dates against records, not only against the CV and the LinkedIn profile.

• For technical candidates, check the public history of their code as well. It carries dates and employer domains.

• Ask in writing, at hiring and every year, for a list of outside roles, investments and advisory work. A role announced in public is not necessarily a role disclosed to the employer.

• Treat a red flag as a question that needs an answer, not as a verdict.

• In an organization that holds sensitive information, do not rely on the check at the door alone. A background check and an internal insider-risk program do different jobs, and both are needed.

It is important to note: he has been charged in a criminal complaint, he has not been convicted, and he is presumed innocent. The facts about the act come from the complaint and are allegations not yet tested in court. The review used public sources only, and the facts are as of 14 October 2026.

Our earlier case study using the same method, on the co-pilot of flight FZ1073: https://profcheck.co/knowledge/case-study-fz1073-copilot/

The full report, with a link to the source of every finding, is available for download.Download the report

Article page
Conflict of interest in the organization: not every conflict is corruption, but every conflict requires attention
Insider Threats & Organizational Risk

Conflict of interest in the organization: not every conflict is corruption, but every conflict requires attention

How do you identify conflicts of interest, what is the difference between a risky situation and improper conduct, and how do you turn background checks and employee declarations into an effective tool for managing organizational risk?

Read full postShow less

A conflict of interest does not necessarily indicate a lack of integrity

A procurement manager at a large company holds shares in one of the organization's suppliers. A candidate for a senior position is married to a manager at a competing company. A CFO is negotiating a future position at a company that has business dealings with his current employer.

What do the three cases have in common?

In each of them, there are circumstances that may create a conflict of interest. But none of the cases, in itself, proves that an offense occurred, that an improper decision was made or that the person involved is dishonest.

This distinction, which seems simple at first glance, is one of the most important distinctions in managing organizational integrity.

In practice, the term "conflict of interest" sometimes triggers an almost automatic reaction of suspicion. Managers are reluctant to declare personal or business ties, candidates fear that a finding in a background check will hurt their chances of being hired, and organizations struggle to distinguish between a risk that can be managed and conduct that requires a substantial inquiry.

The result may be twofold: on one hand, people refrain from reporting relevant circumstances; on the other hand, organizations give excessive weight to the mere existence of a personal or business tie, even when there is no evidence of improper conduct.

A professional approach to conflicts of interest starts with a basic understanding: a conflict of interest is first and foremost a situation that requires examination and management, not proof of wrongdoing.

What is a conflict of interest according to the OECD?

On 28 May 2003, the Council of the Organisation for Economic Co-operation and Development (OECD) adopted the Recommendation on managing conflict of interest in the public service.

The document, Recommendation of the Council on OECD Guidelines for Managing Conflict of Interest in the Public Service, is intended to help countries develop effective policy for identifying, preventing and managing situations in which private interests may influence the performance of a public role.

According to the definition, a conflict of interest exists when there is tension between the public duties of an official and their private interests, in a way that those interests could improperly influence the performance of their duties and responsibilities.

However, the document emphasizes an important distinction even before presenting the definition.

A conflict of interest in itself is not corruption. A conflict that was not identified or not properly managed may develop into a breach of integrity and into improper conduct.

The document adds that when a private interest has already compromised the proper performance of the role in practice, it is more accurate to describe the case as misconduct, as abuse of office or, in the appropriate cases, as corruption.

This is a substantive difference between a situation in which there is potential for improper influence and a situation in which that influence has already materialized.

The distinction is also important from a management perspective: the mere existence of a conflict of interest does not necessarily indicate a personal failure, but failing to identify it, declare it or manage it may create a significant organizational failure.

Source: OECD, Recommendation of the Council on OECD Guidelines for Managing Conflict of Interest in the Public Service, 2003, sections 4 and 10-15.

Three types of conflict of interest every manager should know

The OECD distinguishes between three main categories. The distinction between them helps the organization determine the level of risk and the appropriate way to handle it.

1. Actual conflict of interest

A situation in which there is already a conflict between the official's responsibility and a private interest that may influence the exercise of their authority.

Example: A procurement manager takes part in selecting a supplier while holding a personal financial interest in one of the competing companies.

The holding itself does not prove that the procurement manager gave the company an advantage, but their participation in the selection process creates a conflict of interest that requires handling.

2. Apparent conflict of interest

A situation in which the circumstances create a reasonable impression of possible influence by a private interest, even though in fact there is no such conflict.

Example: A member of an investment committee has the same surname as the owner of a company being considered for investment. This raises a suspicion of a family relationship, but an inquiry reveals that they are not related in any way.

In such a case, an arrangement to prevent a conflict of interest is not necessarily required, but it is important to inquire and to document the findings, in order to prevent unjustified damage to trust in the process.

It is important to distinguish between mere appearance and a situation in which there is a real tie that may create a conflict of interest. When the tie exists, it should not be classified as mere appearance only because the person involved is perceived as trustworthy.

3. Potential conflict of interest

A situation in which there is a private interest that could become a conflict of interest if the official takes on certain responsibility or authority in the future.

Example: An employee holds shares in a company that provides services to the organization, but is not currently involved in decisions concerning that supplier. If they are promoted to a role responsible for selecting suppliers, a conflict of interest may arise.

The management implication is clear: checking the situation at the time of hiring is not enough. It is necessary to identify how a change in role, authority or relationships could change the level of risk.

Actual: The interest conflicts with an existing responsibility. Appropriate organizational response: an immediate arrangement, limiting involvement or another solution.

Apparent: There appears to be a conflict, but an inquiry may rule it out. Appropriate organizational response: checking the facts and documenting the conclusion.

Potential: A conflict may arise in the future. Appropriate organizational response: documentation, monitoring and re-examination when circumstances change.

A private interest is not only money

Organizations tend to focus on financial conflicts of interest: shareholdings, ownership of companies, ties with suppliers or receiving benefits.

These are certainly significant sources of risk, but the professional definition is much broader.

A private interest may also relate to family ties, membership in organizations, additional professional activity, personal commitments, past business ties and even future employment opportunities.

For example:

• A human resources manager who takes part in a decision on promoting a relative.

• A board member who serves at the same time on the board of a company with conflicting business interests.

• An information security manager who advises, for payment, a company that provides services to their organization.

• A vice president who is negotiating a future position at a supplier with which they manage a commercial engagement.

• A project manager who is involved in selecting a contractor owned by a close personal friend.

In some cases the ties are open and known to everyone involved. In other cases they are not known to the organization.

The central question is not whether the tie looks unusual, but whether it may influence judgment, the independence of the decision or the fulfilment of professional responsibility.

Why do honest people also find themselves in conflicts of interest?

One of the common mistakes in risk management is treating a conflict of interest as a character trait.

In management meetings one sometimes hears the claim: "We have known him for years. He is an honest person. There is no conflict of interest here."

But integrity and conflict of interest are two different concepts.

Integrity refers to a person's values and conduct. A conflict of interest refers to the circumstances in which they operate.

A person can have exceptionally high integrity and still find themselves in a situation where personal and professional interests pull in different directions.

In fact, it is precisely people who hold senior positions, with extensive professional experience and a wide network of contacts, who may be exposed to a larger number of such situations.

A veteran manager may know suppliers personally. A director may be involved in several companies. A professional expert may serve as an adviser to other bodies in their field of activity.

These are not necessarily signs of improper conduct. Sometimes they are the natural result of legitimate professional activity.

The organization's challenge is to collect relevant information, assess the risk and create a mechanism that allows people to continue performing their roles while protecting the independence of their judgment.

The paradox of the duty to declare: the more disclosure is punished, the more concealment is encouraged

Many organizations require employees and managers to sign a declaration of no conflict of interest.

At first glance, this is a basic and logical control measure. However, its effectiveness depends to a large extent on the organizational culture.

When an employee understands that the very act of declaring a business or personal tie may harm their promotion, their reputation or their standing, a negative incentive to report may arise.

The risk is not only in a deliberately false declaration. Sometimes an employee does not even know whether a certain tie counts as a conflict of interest, and therefore prefers not to mention it.

Such a reality may lead a mechanism meant to increase transparency to create, instead, a sense of apprehension and uncertainty.

An organization that wants to receive reliable information must distinguish between the act of disclosure itself and a breach of the duty to disclose.

An employee who reports in time a tie that requires examination allows the organization to act in an informed way. By contrast, an employee who knowingly conceals a material tie, contrary to an explicit reporting duty, raises a separate question about their conduct and trustworthiness.

It is also important not to turn the declaration into an immunity mechanism. A late, partial or misleading disclosure is not equivalent to full and accurate reporting at the required time.

The preferred approach is to encourage early and transparent reporting, to clarify which situations must be reported, and to allow employees to get advice when they are not sure whether certain circumstances require a declaration.

From conflict of interest to insider threat: when does the risk materialize?

A conflict of interest is not the same as an insider threat, but in certain cases it may be one of the risk factors for its development.

An insider threat arises when a person with legitimate access to the organization's resources, information or authority uses them in a way that may cause harm, whether maliciously or as a result of negligent or mistaken conduct.

An unmanaged conflict of interest may create circumstances in which an employee makes decisions influenced by a personal interest, uses business information improperly or gives an advantage to a third party.

For example, a manager with a personal interest in a supplier may be exposed to information about the price quotes of its competitors. The existence of the interest does not prove that the information was misused, but the combination of the interest and access to the information creates an exposure that should be examined.

The possible development can be illustrated in four stages:

Stage one: a private interest exists. The employee has a family, business or financial tie that may be relevant to their role.

Stage two: a conflict of interest arises. The employee receives authority or access to information that places the private interest against their duties to the organization.

Stage three: no appropriate management. No arrangement is set, the employee does not report, or the organization ignores the information.

Stage four: possible materialization of the risk. The employee makes a biased decision, passes on prohibited information or uses their authority to grant an improper advantage.

This is not an inevitable path. Most conflict of interest situations do not necessarily lead to improper conduct. But the more material the conflict, the higher the level of exposure and the weaker the control mechanisms, the more important early handling becomes.

From this follows a basic principle in managing insider threats: handling should begin with identifying and managing the risk conditions, not only with investigating incidents after the damage has already occurred.

The role of background checks in identifying conflicts of interest

A professional background check may provide the organization with important information about ties, holdings and roles that do not necessarily come up during a job interview or in the CV.

As part of background checks based on open-source information (OSINT), and subject to the law and to the purpose of the check, it is possible to examine, among other things:

• Holdings and business ties: registered ownership of companies, board positions, partnerships and documented corporate ties.

• Additional occupations: parallel professional roles, consulting activity or other business involvement documented in open sources.

• Ties with suppliers and competitors: affiliations that can be established through records, publications or other reliable sources.

• Employment history: relevant ties to previous employers, related companies or parties with an interest in a transaction.

• Business interests of senior officers: involvement in other companies that may create affiliations with the organization's field of activity.

However, there is a significant limitation: not every private interest is documented in open information.

A family tie that is not public, a personal commitment, an unregistered partnership or confidential negotiations on a new position will not necessarily appear in sources that can be checked.

Therefore, a background check is not a substitute for a declaration by the person being checked, and a declaration is not a substitute for a background check either, when there is a professional and legal justification for carrying one out.

The two tools complement each other: the declaration provides information from the person's side, and the background check can verify some of the information, complete it and sometimes point to gaps that require inquiry.

The most important limitation is that a background check cannot determine, based on the mere existence of a tie, that the person acted improperly.

It can describe a factual finding and help assess the relevance of the tie to the role. The conclusion as to whether an arrangement to prevent a conflict of interest is required should be reached by the authorized party in the organization, after examining all the circumstances.

What should a conflict of interest finding look like in a background check report?

The quality of a background check is not measured only by its ability to locate information. The way the information is analyzed and presented is just as important.

A sweeping statement such as "The candidate is in a severe conflict of interest" may be unfounded if the check did not examine the candidate's areas of responsibility, their authority and the connection between the finding and the role.

On the other hand, ignoring a material business tie only because no evidence of improper conduct was found may miss a relevant risk.

Consider an example.

A candidate for the position of procurement manager is found to be a shareholder in a company that provides services to the hiring organization.

A professional report should separate four questions:

1. What is the factual finding?

The candidate appears as a shareholder in a specific company, according to a defined information source and a given check date.

2. What is the possible connection to the role?

The company operates in a field in which the procurement manager may be involved in decisions on engagements, pricing or supplier selection.

3. What is still not known?

The current shareholding percentage, the extent of business involvement, the candidate's future authority or the existence of a prior arrangement to prevent a conflict of interest may not be known.

4. What is the recommended action?

Obtain the candidate's response, verify missing details and examine whether an arrangement is required that would limit their involvement in decisions concerning that company.

A possible professional wording would be:

"According to the information located, the candidate holds a business affiliation with a company operating in a field relevant to their intended role. The finding may raise a concern of a conflict of interest, depending on the scope of the authority and responsibility to be given to them. It is recommended to clarify the nature of the affiliation and to examine the need for an appropriate arrangement."

Such wording reflects the known information, flags the risk and does not attribute to the candidate conduct that has not been proven.

This is a central difference between a report that provides raw information and a report that helps the organization make a professional and proportionate decision.

How are conflicts of interest managed in an organization? A practical working model

Managing conflicts of interest should not come down to a declaration form signed at the start of employment.

For the system to be effective, it needs to operate throughout the employee's life cycle and include identification, assessment, decision, documentation and control.

Step 1: Mapping sensitive roles

The organization needs to identify roles in which there is a significant risk of conflict of interest.

Usually these are roles that include authority to make financial decisions, access to sensitive business information, supplier selection, recruitment of employees, setting engagement terms or oversight of third-party activity.

The appropriate level of control for a director, a procurement manager or an investment manager is not necessarily the same as that required for an employee who has no material decision-making authority.

Step 2: A declaration of interests adapted to the role

A general declaration stating "I am not in a conflict of interest" may be insufficient.

It is better to ask the employee to answer concrete questions related to the nature of their role, such as business ties with suppliers, holdings in relevant companies, additional occupations or family ties that may influence their decisions.

It is important to explain to the employee that the goal is to identify situations to be managed, and not to assume in advance that there is improper conduct.

Step 3: Verifying and completing information

In roles that justify it, background checks and external information sources can be used to verify relevant data or to complete the picture.

Verification should be focused, proportionate, lawful and relevant to the risks of the role. There is no justification for unlimited collection of personal information only because the employee holds a sensitive role.

Step 4: Assessing the severity of the risk

Not every conflict of interest justifies the same response.

When assessing the risk, it is worth examining the strength of the private interest, the extent of its possible influence, the employee's decision-making authority, the sensitivity of the information they are exposed to and the extent of organizational exposure.

In addition, it should be checked whether there is a practical way to prevent the employee from taking part in certain decisions without significantly harming the organization's functioning.

Step 5: Setting an appropriate arrangement

The solution does not have to be disqualifying a candidate or ending employment.

Depending on the severity of the conflict and the circumstances, solutions such as the following can be considered:

• Refraining from taking part in decisions related to the specific party.

• Transferring decision-making authority to another manager.

• Limiting access to certain sensitive information.

• Changing areas of responsibility or reporting lines.

• Ending an outside business activity that creates the conflict.

• Giving up a relevant financial interest, when this is appropriate and required.

• Disqualification from a specific role when the conflict cannot be managed effectively.

The choice of solution should be proportionate, workable and open to monitoring.

Step 6: Documenting the decision and the responsibility for implementing it

It is not enough to determine that the employee will not take part in decisions concerning a certain supplier.

It is necessary to document the scope of the restriction, who approved it, the person responsible for overseeing it and the cases in which it should be re-examined.

An arrangement that is not documented, or for whose implementation no one is responsible, may remain a statement only.

Step 7: Monitoring and updating

A conflict of interest is not a static situation.

Changes in role, authority, organizational structure, business ties or personal circumstances may create a new conflict or make an existing conflict more material.

Therefore, it is recommended to define events that require an updated declaration and a re-examination, alongside periodic refreshes in sensitive roles.

The important lesson: a conflict of interest can arise even after years of employment

Organizations invest significant resources in the screening and onboarding process, but sometimes assume that once the background check is complete and the declaration of no conflict of interest has been signed, the issue has been dealt with.

This is a problematic assumption.

An employee hired without any conflict of interest may later be appointed to a new role. A relative of theirs may start working at a supplier. A company in which they hold shares may become a contractor of the organization. A change in the supplier base or in the suppliers' ownership structure can also create a conflict that did not exist before.

In such cases, the original background check may be completely correct for the date on which it was carried out, but no longer reflect the current risk.

Hence the importance of an organizational mechanism for updating declarations, re-examining conflicts upon material changes and making focused use of updated checks when this is justified.

The solution is not necessarily to check all employees continuously. Such monitoring may be disproportionate, costly and harmful to privacy. A risk-based approach is preferable, focusing on roles, authorities and events in which there may be a material change in exposure.

What do the OECD findings teach about the gap between policy and implementation?

In the Anti-Corruption and Integrity Outlook 2024 report, the OECD pointed to a gap between the existence of formal rules and arrangements for managing conflicts of interest and the ability of authorities to check the declarations and make sure that the risks are actually addressed.

One of the prominent findings in the report is that only eight of the OECD countries reviewed verified at least 60% of asset and interest declarations in the two years preceding the report.

This does not mean that all the other declarations were wrong, but that the existence of a declaration mechanism does not in itself guarantee the ability to verify the information or to detect gaps.

Although the findings relate to public systems, the management lesson is relevant to business organizations as well.

A declaration form without a mechanism for clarifying findings, settling conflicts and monitoring the implementation of the arrangements may create a sense of security that has no basis.

Similarly, a background check that identifies a relevant business affiliation does not provide full protection if the information does not reach an authorized decision maker or if no practical decision is made on how to handle it.

The effectiveness of a conflict of interest management system is therefore measured not only by the number of declarations collected or the number of checks carried out, but also by the ability to translate the information into decisions and control mechanisms.

Five common mistakes in managing conflicts of interest

First mistake: seeing the declaration itself as an admission of improper conduct.

Such an approach undermines employees' willingness to report and makes early detection of risks harder.

Second mistake: assuming that an honest person cannot be in a conflict of interest.

An assessment of integrity does not replace an examination of the circumstances and of the relevant interests.

Third mistake: settling for a one-time declaration at the time of hiring.

The risk may change during employment and requires an appropriate updating mechanism.

Fourth mistake: treating every business or family tie as automatic grounds for disqualification.

What is required is an examination of the relevance to the role and of the possibility of managing the conflict through proportionate means.

Fifth mistake: treating a finding in a background check as proof of improper conduct.

A finding may point to a situation that requires inquiry, but it does not prove that an improper act took place.

Summary: the test is not the absence of conflicts of interest, but the ability to manage them

Conflicts of interest are an unavoidable part of organizational reality.

People hold financial interests, maintain personal relationships, are involved in additional professional activities and develop business ties throughout their lives. The mere existence of such interests does not necessarily indicate an integrity problem.

The organizational challenge is to identify when a private interest may conflict with professional responsibility, to make sure that the relevant information reaches the authorized party, and to decide how to manage the risk.

OSINT-based background checks have an important role in the process. They may locate affiliations and ties that are not known to the organization, provide a factual basis for risk assessment and help check information provided in declarations.

But the background check is only one component of a broader system, which includes an organizational culture that encourages disclosure, clear procedures, proportionate decision making and ongoing control.

An organization with a developed culture of integrity is not necessarily an organization with no conflicts of interest. It is an organization in which conflicts of interest are identified in time, reported without unjustified fear, examined professionally and managed before they turn into an incident that harms the organization.

And the most important point is that the next conflict of interest in the organization will not necessarily be found in an employee who concealed information.

It may arise precisely in an employee who reported all their ties at the time of hiring, on the day their areas of responsibility, the organization's business ties or their life circumstances changed.

Therefore, managing conflicts of interest is not a one-time act of checking and approval. It is an integral part of managing integrity and organizational governance over time.

Professional sources

1. OECD (2003). Recommendation of the Council on OECD Guidelines for Managing Conflict of Interest in the Public Service. OECD/LEGAL/0316. The original Recommendation, adopted on 28 May 2003, and in particular section 4, and sections 10-15, which define conflict of interest and its types. https://legalinstruments.oecd.org/en/instruments/OECD-LEGAL-0316

2. OECD (2004). Managing Conflict of Interest in the Public Service: OECD Guidelines and Country Experiences. OECD Publishing, Paris. An expanded publication of the guidelines, together with comparative experience from different countries. https://doi.org/10.1787/9789264104938-en

3. OECD (2020). OECD Public Integrity Handbook. OECD Publishing, Paris. Principles for managing conflicts of interest through declaration mechanisms, controls and proportionate arrangements. https://doi.org/10.1787/ac8ed8e8-en

4. OECD (2024). Anti-Corruption and Integrity Outlook 2024, chapter Conflict of Interest. A review of the gaps between regulatory frameworks and implementation, verification of declarations and control in practice. https://www.oecd.org/en/publications/anti-corruption-and-integrity-outlook-2024_968587cd-en.html

This article deals with principles of organizational risk management. The 2003 OECD Guidelines were written for the public service, and the application proposed here in business companies is a management adaptation of their principles. Specific legal obligations, including privacy, employment relations and the duty of disclosure, are subject to the law that applies to the organization and to the officers.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page The original OECD Recommendation (2003)
When an Iranian past disappears from a CV: a risk pattern Israeli companies should know
Insider Threats & Organizational Risk

When an Iranian past disappears from a CV: a risk pattern Israeli companies should know

During background checks we carried out for an Israeli company of strategic importance, we encountered in more than one case a pattern that forced us to stop and take the check deeper.

Read full postShow less

On the face of it, the candidates looked excellent.

They lived in Western countries, had gained experience at well-known international companies and were applying for senior positions. A review of their social media turned up no extremist, anti-Israeli or suspicious activity. A search of open sources and additional databases also found no clear indication of hostile activity.

On the surface, a completely clean profile.

But when we reconstructed their professional timeline in depth, one detail appeared that changed the risk picture: their past included a significant period of employment at an Iranian company identified with the Islamic Revolutionary Guard Corps (IRGC) and subject to sanctions.

After that period, the candidates left Iran, moved to Western countries and worked for several years at legitimate local companies. Only after that geographic and professional distance from Iran had been created did they apply to the Israeli company.

Why the timeline is what matters

A standard background check could end here with the conclusion that there are no negative findings.

That is exactly the problem.

When examining the risk of activity on behalf of a foreign state, one must not look only for "negative information". One must also look for patterns.

The question is not only what appears online about the candidate today. The entire life path has to be examined: where they worked, for whom, in what roles, when they left, where they moved, which professional stops appeared along the way, and when they began to take an interest in Israeli companies or in positions that grant access to sensitive assets.

In the cases we examined, the years of work at Western companies after leaving Iran created, on the face of it, a new and clean professional profile.

This can be seen as an entirely natural career progression. And indeed, that has to be one of the hypotheses examined.

But from the perspective of counterintelligence and insider threat risk management, there is another hypothesis that must not be ignored: those intermediate stops may serve as a layer of separation between a sensitive past and the target organization.

This is the fundamental difference between a "negative information" check and a risk check.

Not everyone who left Iran is a risk

This needs to be said unambiguously.

Iranian origin, past Iranian citizenship, emigration to the West or previous work in Iran are not in themselves an indication of hostile activity.

Millions of Iranians live outside the country, and many of them oppose the Iranian regime.

Origin should therefore not be grounds for disqualifying a candidate.

The significant finding is different: a substantive professional connection to an entity owned by, controlled by or significantly affiliated with the IRGC, especially when it involves a prolonged period of employment or a role that may have required a high level of trust.

Even such a finding does not prove that the person is an Iranian agent.

But it certainly changes the level of risk and justifies an entirely different kind of check.

A "clean profile" is not necessarily an answer

One of the important insights from these cases is that the absence of negative findings online is not necessarily a sufficient indication of the absence of risk.

In the cases we examined, we found no suspicious statements on social media. We found no support for the Iranian regime. No clear unusual activity was found, and no public information appeared linking the candidates to intelligence activity.

Precisely for that reason, the most important finding was easy to miss.

It was not in a Facebook post or an old tweet. It was hidden inside the employment history.

And that is a point Israeli companies operating around the world need to internalize.

Why would an Israeli company be a target?

Certain Israeli companies have intelligence and strategic value that goes far beyond their business activity.

Companies in infrastructure, energy, transportation, technology, cyber, communications, defense, finance, logistics and industry hold information, systems, relationships and access that may be of interest to foreign intelligence actors.

Placing a person in a suitable role may, theoretically, allow access over time to commercial and technological information, to infrastructure and systems, to customers and suppliers, to internal processes, to executives and to people in sensitive positions.

And the goal does not have to be immediate.

A person can be integrated into an organization for years without carrying out a single unusual action. Their value may lie in the very access they accumulate and in the option of using it in the future.

So the question "did we find something they did?" is not always the right question.

Sometimes the question should be: "what is the risk arising from who they were connected to, from the path they took, and from the access they are now asking to receive?"

The broader pattern is a known one

The use of intermediate layers to obscure connections is not a new theory.

In recent years, U.S. authorities have documented time and again the use by IRGC-linked actors of front companies, companies in third countries, intermediaries and commercial identities designed to hide the real Iranian connection. The U.S. Department of Justice has described, for example, the use of companies and intermediaries outside Iran to disguise the role of the IRGC and the origin of certain activities.

In another case, published by the U.S. Department of Justice, a person charged with acting on behalf of the Iranian government obtained a job with a contractor of the U.S. Federal Aviation Administration. According to the indictment, the position gave him access to sensitive information and he passed documents to Iranian actors.

In March 2026, a person who admitted to acting for the IRGC was convicted in the United States. In the course of the proceedings it emerged that he had also been sent to the United States to look for potential recruitment candidates who could remain in the country.

These cases do not prove that any particular candidate for an Israeli company is an agent. They do show that running people, using civilian cover and creating distance between the IRGC and the target of the activity are scenarios organizations need to take into account.

What Israeli companies need to check

When recruiting employees around the world, and especially for senior or sensitive positions, a sanctions check alone is not enough.

The candidate's full professional timeline has to be reconstructed, and the employers themselves have to be checked as well.

Who owns each company they worked for? Who controlled it during the relevant period? Do the company, its parent companies, related companies, shareholders or executives appear on sanctions lists? Is there an affiliation with the IRGC, with the Iranian security establishment or with other government bodies? Are there gaps in the CV? Are there periods that were left out? Does the movement between countries and companies form a natural sequence, or a pattern that calls for further inquiry?

And above all, it is not enough to check the person.

The organizations that shaped their career have to be checked as well.

We are publishing this for one reason

The identifying details in the cases on which this article is based were deliberately changed or omitted to protect the client and the candidates.

The purpose is not to determine that the people who were checked were Iranian agents. We have no evidence that would allow us to determine that.

The purpose is to share a risk pattern that, in our view, Israeli companies employing people around the world must know.

If you are a global Israeli organization, especially one that holds infrastructure, technology, sensitive information or assets of strategic significance, it is worth examining not only the candidates you are recruiting today.

It may be worth looking back as well.

Examining employees who have already been recruited to sensitive positions, re-checking their employment history and asking a question that was not always asked at the time of hiring:

Is there, anywhere along the way, a significant affiliation with an entity controlled by the IRGC or with a sanctioned Iranian entity, even when everything that came after it looks Western, legitimate and completely clean?

Sometimes the most important finding in a background check is not what the candidate did.

It is where they worked, the people they worked for, and the path they took from there to you.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page
The Next Insider Threat Will Not Necessarily Be an Employee
Insider Threats & Organizational Risk

The Next Insider Threat Will Not Necessarily Be an Employee

Over the past month, an unusual series of incidents came to light in which advanced AI models went beyond the test environments they were operating in and carried out independent actions in the real world.

Read full postShow less

These were separate incidents, in different environments and with different models. This was not a coordinated event, and not a "revolt" of AI systems.

But when you connect the patterns of behavior that repeated across the different incidents, a picture emerges that is worth knowing.

The models were given tasks and tried to complete them in the fastest, most efficient way.

In some cases they recognized that the action they were about to take went beyond the instructions or the boundaries set for them, and they continued anyway.

Not out of anger.

Not out of ideology.

And not because they developed a "desire" to cause harm.

Simply because the action helped them complete the task.

And that is exactly what makes these incidents so significant.

In some of the cases, covert patterns of behavior were observed.

Deleting logs.

Modifying test code.

Attempting to hide actions from oversight mechanisms.

Using proxies and anonymous browsing tools.

And even creating communication channels that allowed different agents to pass information between them.

In other cases, the agents moved from activity inside their own computing environment to interaction with the outside world.

They carried out actions against computer systems.

Collected information.

Looked for vulnerabilities.

Used fake identities.

Performed social engineering.

Tailored approaches to specific people based on the information they found about them.

And in some scenarios, several agents even shared information, divided tasks and helped one another.

This, in my view, is where the real risk picture begins.

We are used to thinking of an insider threat as a person inside the organization.

An employee.

A manager.

A contractor.

A supplier.

A person who received legitimate access to systems, information or processes, and at some point uses that access in a way that harms the organization.

But now a new actor enters that same equation.

An AI agent.

It too can live inside the system.

It too can receive legitimate permissions.

It too can access sensitive information.

It too can operate tools.

It too can make decisions.

And it too can take actions without a human approving every step.

The difference is in speed and scale.

One employee can perform a limited number of actions in a given amount of time.

An AI agent can perform hundreds or thousands of actions, explore several directions in parallel, activate additional tools and communicate with other systems in a very short time.

And if several agents operate together, we already need to think about something entirely different.

Not a single agent.

But something like a swarm.

A group of agents that can divide tasks, pass information and act in parallel.

That can be a very powerful working tool.

But for exactly the same reason, it can also be a very significant threat.

Which leads to another conclusion:

We do not need to wait for "conscious" AI to face a real risk.

A system does not need emotions, free will or malicious intent to cause damage.

It is enough that it can plan.

Act.

Find creative ways to reach a goal.

Work around obstacles.

And use the permissions it was given in ways nobody planned for.

From the organization's perspective, the outcome can be the same outcome.

Data leakage.

Disruption of systems.

Harm to customers.

Unauthorized access.

Fraud.

Or a new attack path created from inside the organization itself.

And this is the point where, in my view, the concept of the insider threat has to change.

In the world we are entering, it is not enough to ask who our employees are and who our suppliers are.

We need to start asking as well:

Which AI agents operate inside the organization?

Which systems do they have access to?

What permissions were they given?

What information can they read?

What actions can they perform?

Can they reach outward?

Can they activate additional tools?

Can they communicate with other agents?

Who supervises them?

And what happens if they decide that the most efficient way to complete the task runs through an action we never meant to allow?

These are no longer theoretical questions.

These are risk management questions.

And I estimate that before long, organizations will need to treat bringing an AI agent into the work environment almost the way they treat bringing in an employee, a supplier or a system with sensitive permissions today.

Not because an AI agent is an "enemy".

But because it becomes an active player inside the organization.

A player you need to know.

Understand.

Limit.

Monitor.

And assess for risk before it is given access.

Not because we think the entry of AI agents into organizations can be stopped.

The opposite.

They will come in.

The question is whether we bring them in the way we used to bring in ordinary software, or understand that this is an operational entity that receives trust, permissions and the ability to act inside the organization.

In the new world of insider threats, the question will no longer be only:

Who is inside the organization?

But also:

What operates inside it, what permissions did we give it, and what can it do when it is left alone.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page
The Most Dangerous Employee Has Already Handed In a Resignation Letter
Insider Threats & Organizational Risk

The Most Dangerous Employee Has Already Handed In a Resignation Letter

The most dangerous employee in your organization is not the one who failed the background check. It is the one who has already handed in a resignation letter.

Read full postShow less

In 2016, a senior engineer left Google's self-driving car project to start his own company. His name was Anthony Levandowski. In the months before he left, he downloaded around 14,000 technical files from the company's servers. The rest is well known: a massive lawsuit between Waymo and Uber, a settlement worth hundreds of millions of dollars, and a criminal conviction for trade secret theft. All of this happened at a company with one of the most sophisticated security operations in the world.

Most organizations treat a resignation as an HR event: a letter, a conversation, a handover, cake on the last day.

In practice, from the moment an employee gives notice, and sometimes earlier, while the decision is still taking shape in their head, the equation has changed: their access to systems remains full, but their commitment is already at their next job.

This window, between the notice and the last day, is the highest-risk period in the entire employment cycle. And it is not only about dramatic theft. It also looks like this: copying a client list for personal use. Sending pricing documents to a private email address to keep work samples. Photographing methodologies the employee wrote themselves and therefore assumes are theirs. And sometimes with no bad intent at all: a cloud account left open for months after the departure, because nobody knew it existed.

The organizational problem is easy to state: HR knows first, the security manager hears last, and IT cuts off access on the last day. Nobody owns the window itself.

Here is how to close it. Six steps:

1. The day of notice is the day of reporting. A resignation letter reaches the security officer and IT the same day. Not at the end of the week, not once a date has been set.

2. Immediate access mapping. Which systems, databases and folders the employee can reach, and which of them are especially sensitive given where they are going.

3. Gradual reduction. Anything not required for the handover is closed now, not on the last day.

4. Monitoring the window. Unusually large downloads, transfers to a private email address, connection of portable devices. During the window this is not suspicion, it is the best-known point of exposure.

5. Tasks for the last day. A closed list of accounts to shut down, including cloud systems and external vendors that are not connected to central user management. Those are the ones always forgotten.

6. A proper exit conversation. A reminder of confidentiality and intellectual property obligations, and an open discussion about where the person is heading next. Not out of suspicion, out of risk management.

The other side matters too: most leavers are not a threat. An employee who leaves well is an asset, an ambassador, sometimes a future client. Managing the window properly is not about turning every leaver into a suspect. It is the opposite: letting the good ones leave on good terms, and catching in time the rare case that costs the organization a fortune.

Recruitment knows exactly when an employee joins the organization. The question is who owns the moment they leave.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page
The brilliant startup that can't work because it has no security clearance
Insider Threats & Organizational Risk

The brilliant startup that can't work because it has no security clearance

In recent years I've been hearing more and more defense organizations talk about their desire to work with small, innovative and agile companies. Everyone wants innovation. Everyone wants creative solutions. But in reality, quite a few companies never even make it to the starting line.

Read full postShow less

An interesting article published recently in the UK exposed one of the biggest challenges in the defense world: the security clearance process itself.

On the one hand, there's no debate about the importance of background checks, security clearances and protecting sensitive information. These are essential mechanisms designed to safeguard national interests, sensitive technologies and critical supply chains.

On the other hand, when the process of obtaining a clearance drags on for many months and sometimes more than a year, an absurd situation arises: the company can't get a contract because it has no clearance, but it also can't get a clearance because it has no contract.

This dilemma isn't unique to the UK. Anywhere that complex screening processes and trustworthiness vetting exist, the challenge is finding the balance between security and agility.

As someone who has worked for many years in the field of background checks and trustworthiness vetting, I believe the goal is not to lower the requirements. On the contrary.

The goal is to create smarter, faster and risk-management-based processes.

Not every supplier represents the same risk. Not every employee needs the same level of vetting. And not every process has to drag on for many months.

When risks are managed properly, you can both maintain security and enable innovation and growth.

The real challenge isn't to perform more checks. The challenge is to perform the right checks, at the right time, and in a way that lets the organization move forward instead of getting stuck.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page Read the article
Would you let someone who stayed silent in the face of murder treat you?
Insider Threats & Organizational Risk

Would you let someone who stayed silent in the face of murder treat you?

I read the article about Lihi Darnell (Gluzman), the state's witness in the Asaf Steierman murder case, who is now undergoing training in clinical psychology. Beyond the legal and public debate, this case raises in my eyes a far broader professional question:

Read full postShow less

How deeply do organizations vet the people in whose hands they place power, influence and trust?

In this case it's a therapeutic profession. In other settings it's a CFO, a security officer, a procurement manager, an IT person with broad permissions, or an employee exposed to sensitive information.

One of the central lessons from the world of insider threats is that not every risk is measured by a criminal record or a conviction. Sometimes it's precisely behavioral patterns, decision-making under pressure, moral judgment and reactions to extreme events that should set off warning lights.

Many organizations focus on the question "Does this employee have a criminal record?", but often the more important question is: "Is there material information about their past conduct that would make us think twice before granting them a sensitive role?"

In this specific case, it isn't a legal question but a question of risk management.

When a person is set to hold a position of trust, to influence other people or to gain access to sensitive resources, it's worth examining several layers: a history of decision-making in extreme situations; involvement in events of public or moral significance; gaps between their current image and material past events; an up-to-date rather than one-off risk assessment; and oversight and control mechanisms over time.

It's also important to remember that insider threats don't arise solely from malicious intent. Sometimes they stem from poor judgment, from withholding information, from a lack of accountability, or from value conflicts that weren't identified in time.

Ultimately, every organization has to decide where the line lies between personal rehabilitation and professional responsibility. It's a complex decision, but it must be made out of informed risk management and not out of the assumption that if there's no legal impediment, there's no risk either.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page Read the article
He looked like the perfect employee, until he started to dismantle the organization.
Insider Threats & Organizational Risk

He looked like the perfect employee, until he started to dismantle the organization.

One of the most disturbing books we have read recently in the field of organizational behavior is "Snakes in Suits: When Psychopaths Go to Work" by Paul Babiak and Robert Hare.

Read full postShow less

The book deals with the kind of people that most organizations don't really know how to identify in time. Not violent criminals. Not extreme characters from movies. Rather charismatic, impressive, sharp people, with an extraordinary ability to make others believe in them.

It is precisely because of this that they are dangerous.

The authors describe how an organizational psychopath manages to fit into an organization, advance quickly, accumulate power and influence, and along the way leave behind enormous damage: the breaking up of teams, the creation of conflicts, political manipulations, intimidation of employees, harm to trust, the creation of a toxic culture, and at times also fraud and abuse of authority.

What is particularly interesting is that the book explains that the problem is not only with the person himself. At times the organization also contributes to it without realizing it.

Organizations that sanctify charisma, fast results, aggressiveness, achievement at any cost, and internal politics, may mistakenly identify psychopathic behavior as "leadership".

One of the important things in the book is the description of the three stages in which an organizational psychopath operates.

In the first stage he studies the system: who is strong, who is weak, who is influential, who is threatened, who has access to power and information.

In the second stage the manipulation begins: flattery, the creation of false trust, adapting his personality to each individual, sophisticated lies, and quiet harm to rivals.

In the third stage comes the abandonment: when the person is no longer useful, he is thrown aside. Sometimes also with deliberate harm to his reputation.

The most important part for me is the understanding that it is not always possible to identify such people through charisma or first impression. On the contrary.

In many cases they are calm under pressure, know how to speak convincingly, project self-confidence, know how to "read people", and imitate empathy excellently.

And therefore in the world of Insider Threats, employee recruitment, and reliability assessment, one must not rely only on intuition or a "gut feeling".

One must examine: behavioral consistency, gaps between words and actions, patterns of manipulation, attitude toward people without power, history of conflicts, and repeated use of victims, accusations, and politics.

This book is an excellent reminder that the most dangerous threats in an organization don't always come from outside.

Sometimes they are sitting in the boardroom.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page
The most dangerous manager in the organization? It isn't always the one who steals information
Insider Threats & Organizational Risk

The most dangerous manager in the organization? It isn't always the one who steals information

I meet quite a few managers who look at the 'insider threat' only through the prism of information theft, industrial espionage or financial fraud. But there is another kind of insider threat, far quieter, that usually does not appear in security reports.

Read full postShow less

The abuser.

That manager who belittles employees, humiliates them in front of others, instills fear, erodes them psychologically, creates anxiety and dismantles self-confidence over time.

Studies have already shown that workplace abuse does not stay on the emotional level alone. It harms cognitive ability, decision-making, memory, concentration and professional functioning. An employee under ongoing psychological terror begins to make more mistakes, to withdraw, to lose motivation and sometimes even to develop anger toward the organization itself.

And this is exactly where the connection to the world of insider threats begins.

Because sometimes the 'predator' himself is the insider threat. And sometimes he creates a new insider threat: the employee he has harmed.

An employee who experiences ongoing humiliation can turn into a bitter, indifferent, vengeful or uncommitted person. In certain cases this manifests as quiet quitting, leakage of information, harm to processes, or simply a functional collapse that damages the organization from within.

This is exactly why I think it is not enough to check only the integrity, past or reliability of candidates. You also need to know how to identify predatory patterns.

Yes, there are ways to identify them. You can detect early signs already at the recruitment stage: extreme patterns of control, manipulativeness, lack of empathy, destructive interpersonal relations over time, recurring burnout patterns in the teams they have managed, and a work environment that produces fear instead of trust.

And if that person is already inside the organization, you must monitor such behaviors exactly as you monitor other security anomalies. Because their damage does not always appear immediately, but when it explodes, the organizational cost is enormous.

I think that in the near future organizations will understand that workplace abuse is not only an issue of HR or employee well-being. It is an issue of organizational security.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page
Phishing doesn't only steal passwords. Sometimes it steals sensitive technology.
Insider Threats & Organizational Risk

Phishing doesn't only steal passwords. Sometimes it steals sensitive technology.

The story published by NASA's Office of Inspector General should worry every organization that holds sensitive knowledge, code, software, engineering designs or valuable business information.

Read full postShow less

According to the publication, a Chinese citizen named Song Wu posed for years as American engineers, researchers and professors, and approached NASA employees, academic researchers, military personnel and private companies. His goal was not to obtain a password to an account. He asked for something far simpler and far more dangerous: copies of software, source code and sensitive engineering tools that could be used for aeronautical design and the development of weapons systems.

And that is exactly the point.

In many organizations, when people hear the word 'phishing', they immediately think of an email with a suspicious link, a fake website or a request to enter a password.

But in more sophisticated cases, phishing does not look like a cyberattack. It looks like a legitimate professional request from a familiar person. 'Please send me the code'. 'I need the latest version of the software'. 'Send me the file, I'm working on it with the team'.

The victim doesn't feel they are falling for an attack. They feel they are helping a colleague.

And that is precisely the danger.

The professional mistake I see again and again is that organizations treat this threat only as a technological problem. But in this case, the central weakness was not only in the system. It was in human trust, in the work culture, and in the absence of a clear mechanism that requires stopping and checking before sensitive information goes out.

As I see it, there are several important lessons here.

Not every request that comes from a 'familiar' person really comes from them.

Not every sharing of information between colleagues is an innocent act, especially when it involves code, software, plans, data, models or infrastructure.

Employees need to know how to recognize not only suspicious links, but also unusual requests: repeated requests for the same software, no explanation of why the information is needed, a sudden change in the payment or transfer method, the use of unconventional channels, or pressure to hand over material without an orderly process.

And most importantly: in a serious organization, an employee should not decide alone whether sensitive material may be transferred to another party, even if that party appears familiar, senior or professional.

You need a procedure. You need identity verification. You need a permissions check. You need an understanding of the limits of regulation, export, confidentiality and intellectual property. And you need a culture in which stopping to check is not seen as bureaucracy, but as part of professional responsibility.

The NASA story is a sharp reminder that an insider threat does not always begin with a malicious employee. Sometimes it begins with a good, professional employee who wants to help, but doesn't realize they are being manipulated.

And that may be one of the most dangerous threats of all: a human Trojan horse that doesn't know it is one.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page Read the article

Behavioral Profiling & Vetting

The body betrays long before the words break
Behavioral Profiling & Vetting

The body betrays long before the words break

One of the most fascinating topics in the world of human behavior is the Embodiment Effect.

Read full postShow less

The core idea is simple but very profound: our body does not merely "express" emotions and thoughts, it also influences them, and sometimes even reveals them before the brain manages to control the message.

For years, body language was viewed as an "add-on" to communication. Today it is already clear that it is part of the thinking system itself. Sitting posture, hand placement, breathing rate, head movements, distance from the camera, use of space, micro-expressions, vocal changes, and even the manner of typing are all part of a behavioral information system.

In business profiling this is critical.

When we conduct a reliability assessment or try to identify the potential for an internal threat within an organization, we are not looking only for a "lie." It is far more complex. We are looking for incongruence.

The Embodiment Effect makes it possible to understand when physical behavior is not synchronized with the narrative a person is trying to produce. For example: a candidate who speaks confidently but whose body is in continuous defensiveness; an employee who declares commitment to the organization but reacts physically with stress when issues of authority, control, or loyalty arise; a manager who presents stability but shows abnormal signs of arousal around financial questions or internal conflicts; a remote candidate who produces "too perfect" eye contact, with an artificial response pace and communication patterns that suggest the use of external aids or real-time AI.

And here the new challenge enters: remote assessment.

In the era of hybrid work and Zoom interviews, some people think it is possible to "hide" behavior through a screen. In practice, the opposite sometimes happens.

The camera reduces background noise and forces us to focus on micro-behaviors: response delays, tone changes, eye darting, over-adjustments, unnatural listening, disconnects between voice and expression, motor freezing, and excessive use of calculated gestures.

Precisely in a remote environment, when you know what to look for, you can identify very significant indications of reliability, stress, concealment, manipulation, or internal conflict.

But it is important to state the professional truth: there is no "magic sign" that proves a lie. This is one of the biggest mistakes in the field.

Professional profiling is not built on myths of "touching the nose = lying." It is built on creating a behavioral baseline, identifying anomalies, cross-referencing information sources, analyzing context, understanding motivations, and reading dynamics rather than just isolated signs.

The Embodiment Effect is especially important in identifying internal threats within organizations, because people can control their words far more than their bodies. And in situations of stress, conflicting loyalties, a sense of threat, or concealment, the body almost always "leaks" information.

The future of the world of business profiling will not be based solely on technology nor solely on human intuition. It will be a combination of deep behavioral understanding, digital analysis, the use of OSINT, anomaly detection, and the human ability to read people even through a screen.

Because in the end, even in the era of AI, a person still leaves a behavioral signature.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page
Not every toxic employee shouts. Some just smile right in the interview.
Behavioral Profiling & Vetting

Not every toxic employee shouts. Some just smile right in the interview.

One of the most troubling topics in the world of personality assessment is 'the Dark Triad'.

Read full postShow less

These are three personality traits that may initially look like self-confidence, charisma, or assertiveness, but within an organization they can turn into a real internal threat: narcissism, which involves a need for admiration, a sense of superiority, and difficulty accepting criticism; manipulativeness (Machiavellianism), which means using people as tools to achieve goals, without much guilt along the way; and functional psychopathy, which involves extreme coolness, a lack of empathy, and the ability to carry out harmful actions without conscience.

The interesting part is that people with such traits don't always fail job interviews. On the contrary.

More than once they are very impressive. They know how to talk. They know how to sell themselves. They know how to identify other people's weaknesses. And they know exactly which persona the organization wants to see in front of them.

That's why I think one of the biggest challenges today in the world of insider threats is not only identifying a 'problematic past', but understanding patterns of personality and behavior that may turn into an organizational risk in the future.

This can manifest as leaking information, deliberately harming the organization, manipulating employees, creating a toxic culture, or simply making dangerous decisions without any empathy for the consequences.

It's clear that not every person with Dark Triad traits is a criminal or an insider threat. But when you combine access to sensitive information, pressure, ego, lack of oversight, and manipulative ability, you get a combination that managers must be aware of.

And this is exactly where the value of in-depth assessment, proper questioning, intelligence from open information sources, and identifying red flags before harm occurs comes into play.

Because in the end, the most dangerous threat in an organization is usually not the one who looks dangerous. It's the one who knows how to look perfect.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page
Culture shapes the person standing in front of us
Behavioral Profiling & Vetting

Culture shapes the person standing in front of us

When we assess a person, it is very easy to project our own value system onto them. What looks to us like suspicious, inconsistent, or even problematic behavior can, in another context, be perfectly normal.

Read full postShow less

For example, there are cultures in which avoiding eye contact is a sign of respect. For others, it immediately raises questions. There are places where direct communication is seen as positive, while elsewhere it is perceived as rude.

And this is where biases come into play.

When we are not aware of them, we are not really analyzing the person. We are analyzing the gap between them and us.

In business profiling, this is especially critical. Decisions are made about people: candidates, partners, suppliers. An error in interpretation can lead to missing out on an excellent person, or worse, to failing to identify a real risk.

So what do we learn from this?

First of all, professional humility. Understanding that not everything that seems right to us truly is.

Second, context. Always asking: where does this person come from? Does the behavior fit with the culture they come from?

And finally, the right combination of analytical tools and human understanding. Without this, there is no real objectivity.

Anyone who works with people must understand cultures. Otherwise, they are simply guessing.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page
Is Enshittification a bad thing? Not always.
Behavioral Profiling & Vetting

Is Enshittification a bad thing? Not always.

Enshittification = the extreme degradation of something into a worse version of itself.

Read full postShow less

I remember a time when LinkedIn was a very "clean" place. Professional, calculated, a little sterile. Everyone wrote the same things, everyone sounded the same, and there was almost nothing there that truly revealed who the person behind the profile really was.

And then the enshittification began.

More personal posts. More politics. More extreme opinions. More provocations that gain exposure because the algorithm loves noise.

For anyone looking for a purely professional platform, this looks like deterioration. And to a large extent, it really is.

But from my perspective, something interesting happened here.

It is precisely this "out of place" content that begins to tell the real story.

When I check someone as part of a background check from open sources, I'm not just looking at what they do. I'm looking at how they think. How they react. What sets them off. Where their boundaries are.

And these things almost never showed up on the old LinkedIn.

Today they are there. In abundance.

A political post written without filters, an aggressive response to a professional discussion, a choice to join a provocative trend, these are no longer "noise" to me. They are signals.

What was once a barren wasteland in terms of understanding personality has become a gold mine of behavioral indicators.

So yes, LinkedIn has changed. And maybe not for the better for those looking only for professionalism.

But for those who understand how to read between the lines, it's a platform that tells far more truth than it did before.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page

AI, Deepfakes & Synthetic Fraud

AI, Deepfakes & Synthetic Fraud

The lineup that never happened: Deepfake as an insider threat to the organization

The people in this video were not arrested. But the video illustrates a problem that every security manager, HR manager and CEO must be aware of.

Read full postShow less

In the video above, the likenesses of Sam Altman, CEO of OpenAI, Dario Amodei, CEO of Anthropic, Mark Zuckerberg and Donald Trump, with Jensen Huang facing them, appear standing in a police lineup and singing together.

The situation is absurd, the result is amusing, and the video looks remarkably believable.

But no such lineup ever took place. The video was created with artificial intelligence as part of a satire of the AI industry.

The video was posted on X by Matthias Schmidt (@eurofounder) on 16 October 2026: https://x.com/eurofounder/status/2111122495667413424

I watched it and actually thought about something completely different: what happens when the ability to produce such a convincing reality meets the world of organizational trust and integrity?

Until recently, a photo, a voice recording and certainly a video call were considered significant evidence that a particular person had actually said or done something.

Today, that assumption is no longer safe.

We are entering a period in which it is possible not only to fake an identity, but also to generate for that identity behavior, a voice, facial expressions and interaction that look completely authentic.

And this is no longer just a problem of spreading false information. It is a real risk to organizational security.

From an external threat to an insider threat

Consider three scenarios:

A candidate for a sensitive position goes through a video interview using a false identity, with a face, voice and professional background that are not their own. The organization is convinced it has hired a specific person, but in practice it grants permissions and access to someone else.

A finance manager receives a video call from someone who looks and sounds exactly like the CEO, with an urgent instruction to transfer money or sensitive information. The employee carries out the instruction in good faith, and the organization is harmed from within.

And a video of an employee, circulating online, that purportedly documents criminal behavior, an extremist statement or an information leak. The organization rushes to conclusions, even though the event never took place.

In each of these cases, the technology allows an outside party to exploit the trust, processes and permissions of people inside the organization.

This is how a threat that originates outside the organization may turn into an insider threat incident.

Check the story, not just the video

And here the truly important question arises:

If we can no longer rely on what we see and hear, what can we rely on?

In my view, the answer lies in changing the method of checking.

Instead of asking only whether the video is real, we need to ask whether the story behind it is real.

This is where background checks and open-source intelligence (OSINT) become important.

A professional OSINT check does not settle for analyzing a single image or video. It examines the wider context and connects information from different sources, preferably independent ones, to build a more reliable picture.

For example:

1. Checking the source of the information: Who first published the video? When? Can the original source of the distribution be traced, and not just dozens of shares of the same content?

2. Verifying identities: Does the person appearing in the video match their digital identity over time? Is there a consistent professional history, social media activity, connections and external data that support their identity?

3. Cross-checking sources: Is there independent evidence of the alleged event? Do the dates, places, people and circumstances fit with other information that can be verified?

4. Examining activity patterns: Is there a gap between known digital behavior and an unusual event? Have new accounts, identity changes or deliberate attempts to create a false impression appeared recently?

5. Understanding the context and possible motives: Who is behind the distribution, what is their operating environment, and are there indications of an attempt to mislead, influence or cause harm?

It is important to stress: OSINT is not a magic solution. Open sources can also be fake, coordinated or mistaken. And the absence of findings does not prove that a person or a video is authentic.

But the more independent sources are cross-checked and the sequence of events is examined, the harder it becomes to base a fraud on a single fake piece of information.

And that is exactly the advantage of examining the big picture.

What to change in procedures

Alongside intelligence checks, organizations must also adapt their procedures: verify unusual instructions through an independent communication channel, apply dual control to sensitive actions, verify identities in recruitment processes, and avoid making decisions based on a single video.

This means that the responsibility for telling truth from forgery can no longer rest only with our own eyes, or with software that tries to detect Deepfakes.

It requires critical thinking, cross-checking of information and an understanding of the human, professional and organizational context.

The video above was meant to be funny. And it really is funny.

But it also illustrates how easy it will be to present us with a reality that never existed.

In an era when almost everything we see and hear can be faked, trust cannot rest on how convincing the evidence is. It must rest on the ability to verify it through additional evidence.

And this, in my view, is one of the most important changes that needs to happen today in the world of organizational integrity and security.

The professional basis for the recommendations

The recommendations in this article are based on three publications by US government bodies:

1. The joint publication by NSA, FBI and CISA (September 2023). The document Contextualizing Deepfake Threats to Organizations: Deepfake threats to organizations, and ways to prepare for, identify, defend against and respond to them. https://www.cisa.gov/news-events/alerts/2023/09/12/nsa-fbi-and-cisa-release-cybersecurity-information-sheet-deepfake-threats

2. The NIST AI 100-4 document (November 2024). Reducing Risks Posed by Synthetic Content: an overview of content provenance verification, labeling and detection of synthetic content, and the limitations of these technologies. https://www.nist.gov/publications/reducing-risks-posed-synthetic-content-overview-technical-approaches-digital-content

3. NIST's Guardians of Forensic Evidence program. A program for evaluating automated Deepfake detection tools. According to NIST, there is a gap between high accuracy in research and the difficulty of applying the tools in the real world. https://www.nist.gov/programs-projects/guardians-forensic-evidence

Tips for spotting deepfakes, with a source for every recommendation, are available as a two-page document.Download the tips

Article page The joint NSA, FBI and CISA publication
The Human Eye Is No Longer an Identity Verification Tool
AI, Deepfakes & Synthetic Fraud

The Human Eye Is No Longer an Identity Verification Tool

I found a small game called Slopcheck that is worth a few minutes. The idea is simple: every day it shows six images, and we have to decide whether each one is a real photo or an image generated with AI. After every answer the game explains which details in the image could have given it away.

Read full postShow less

Sounds easy? I suggest trying it before you answer.

But for me, this game is interesting for a completely different reason. It illustrates a problem we run into today in background checks and OSINT: we still put too much trust in what we see.

A professional photo on LinkedIn. An Instagram account that looks active. A photo of someone at a conference. A profile that looks long established. Photos with friends, family or colleagues.

Once, a set of signals like that gave us the feeling that a real person stood behind the profile. Today that is no longer enough.

You can generate a face that never existed. You can create images of the same person in different settings. You can build a visual history that looks convincing. And you can wrap a fake identity in a professional profile that looks, at first glance at least, completely credible.

And that is exactly the trap.

Sometimes we go looking for the AI tell: an extra finger. Garbled text in the background. A shadow that does not line up. Odd glasses. Anatomy that makes no sense.

These tells matter, and the game is excellent for training the eye. But professionally, I do not think this is the right way to handle the problem. Because as the models improve, the visual tells we learned to spot disappear.

So in a background check the question should not only be: was this image generated with AI?

The more important question is: does the identity behind the image hold up against reality?

And at that point you have to move from a single image to checking the whole picture.

Does the professional history add up? Are there independent indications tying the person to the organizations they claim to have worked for? Is their timeline plausible? Does the activity across different networks match? Do real professional connections indirectly confirm the story? Do photos, mentions, documents and separate profiles form one consistent identity, or do they contradict each other?

That is the difference between looking at a photo and verifying an identity.

In the age of AI, human intuition still matters a great deal. But it should be the starting point of an investigation, not the verification mechanism itself.

And that may be the most important lesson from Slopcheck: if we get an image wrong in the game, we lose a point. If an organization gets the person behind a profile wrong, the price can be something else entirely.

It is worth trying the game and seeing how good you really are at this.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page Link to the game
When the face on the screen is real. The person behind it isn't.
AI, Deepfakes & Synthetic Fraud

When the face on the screen is real. The person behind it isn't.

This past week, a particularly troubling case came to light in Israel that shows how the world of fraud is being transformed by artificial intelligence.

Read full postShow less

According to the suspicions, a 20-year-old managed to create “synthetic identities” of Israeli citizens using photos and personal details obtained from breached databases. With AI tools he animated the photos, produced videos that looked entirely authentic, and used them to open bank accounts, order credit cards and carry out financial transactions in the names of people who had no idea it was happening.

According to the investigation, many dozens of victims have already been identified, and it is suspected that hundreds of citizens were harmed by this activity.

What troubles me most about this case is not only the scale of the fraud, but the proof that the identification methods we have relied on for years are no longer sufficient on their own.

A photo of an ID card, a selfie, a short video, remote verification — until recently all of these were considered strong layers of protection. Today, in the right hands and with advanced AI tools, they can be faked to a level that makes it very hard for the human eye to detect the deception.

This challenge no longer belongs only to banks. It is relevant to any organization that hires employees remotely, approves suppliers, opens customer accounts, grants access permissions or runs digital identification processes.

The question is no longer whether an identity can be faked, but whether your control system is able to detect the forgery in real time.

In recent years I have seen more and more cases in which the line between a real person and a figure created by AI is becoming blurred. Organizations must adapt their verification mechanisms to the new reality, and not rely solely on methods built for a world that existed before artificial intelligence.

Alongside the threat, there are now advanced solutions that make it possible to spot signs of AI forgeries, detect anomalies in the identification process and verify identities in real time.

We have advanced technological solutions to address these challenges in real time. Feel free to reach out to me for details.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page Read the article
How do we know if what we're seeing is really happening or really happened?
AI, Deepfakes & Synthetic Fraud

How do we know if what we're seeing is really happening or really happened?

This is no longer a philosophical question. It's a business question, a security question and a management question.

Read full postShow less

The article in Science by Prof. Hany Farid, one of the world's leading experts on detecting digital manipulation, lays out a reality we all have to internalize: a deepfake no longer looks like a technological toy. It looks real, sounds real, spreads fast, and shapes the way people make decisions.

And the big problem isn't just that the fakes are getting better. The bigger problem is that trust is being eroded.

When a manager receives a video. When the HR department runs an online interview. When a company gets approached by an investor, a candidate, a vendor or a business partner. When an incriminating video starts circulating online. When a familiar voice asks for urgent action.

The first question can no longer be: "Does this look real?" Because today, plenty of fake things look completely real.

The right question is: "How do we check this professionally before we act?"

What I especially liked in the article is Farid's investigative approach. He doesn't settle for an automated tool that says "90% fake" or "70% real." He examines physics, motion, shadows, reflections, angles, lip-sync to voice, consistency between frames, and the broader context.

And that's exactly the point. With deepfakes there is no single magic solution. You need a combination of technology, investigative experience, an understanding of human behavior, an understanding of the digital arena, and the ability to ask the right questions.

In the business world this is especially critical. Because deepfakes don't threaten only politicians or celebrities. They threaten hiring processes, background checks, trust between organizations, fraud protection, digital identity, and the ability to understand who is really standing in front of us.

An online job interview can be faked. A professional profile can be well built yet not genuine. A manager's voice can be cloned. A video can be edited. An image can be generated from scratch. A document can look authentic while being part of a broad deception scheme.

That's why organizations can't stay at the stage of "it looks real to me." They need a verification capability. Not out of panic. Not out of excessive suspicion. But out of responsibility.

Anyone who recruits employees for sensitive roles, vets business partners, verifies identities, handles fraud incidents or deals with suspicious content online must add to their desk the ability to deal with deepfakes too. Especially when everything happens online.

If you're dealing with a suspected deepfake, a fake identity, a suspicious interview, problematic digital content or an incident where it's unclear what's real and what's not, you're welcome to reach out to us.

We have innovative, groundbreaking solutions for dealing with deepfakes, including in online environments, combining advanced technology with professional human analysis.

Get these breakdowns in your inbox, plus the six steps for closing the offboarding window as a one-page brief.Get the one-pager
Article page Read the article
AI, Deepfakes & Synthetic Fraud

If a face can be faked at the click of a button, how do we know who is really sitting across from us?

One of the greatest challenges in the world of modern recruitment is the fact that we no longer truly know whether the person appearing on screen is who they claim to be.

Read full postShow less

AI tools are now available to anyone and make it possible to alter appearance, voice and even an entire identity in real time. What was once the domain of intelligence agencies or film studios has become an accessible tool that can be run from a home computer.

The implication for organizations is clear: a video interview is no longer a sufficient means of verifying identity.

In recent years, the world has seen quite a few cases of candidates impersonating other people, using fabricated identities or concealing material information during the recruitment process. As Deep Fake technologies become more convincing, the risk grows accordingly.

This is precisely why background checks based on open-source intelligence (OSINT) are becoming an increasingly significant part of recruitment processes, especially for sensitive roles.

When you examine a candidate's digital footprint over time, cross-reference different sources of information and verify the consistency between the presented identity and the real digital presence, you can identify gaps and warning signs that would never surface during an online interview.

The technology that makes it possible to hide the truth is advancing rapidly.

The challenge for organizations is to ensure that the tools for revealing the truth advance at the same pace.

Tips for spotting deepfakes, with a source for every recommendation, are available as a two-page document.Download the tips

Article page
Stay sharp

Get our insights in your inbox.

New cases, red flags and reliability lessons - a short email when something worth reading goes up. No spam, unsubscribe anytime.